Government software,delivered on deadline.
We help federal, state and local agencies launch modern citizen portals, replace legacy systems and pass compliance audits on schedule.
Built for how government actually buys and runs software.
Digital Service Modernization
We replace legacy citizen portals, paper workflows, and disconnected systems with modern, mobile-responsive platforms. Every engagement follows Digital Services Playbook principles: user research first, iterative delivery always, measurable outcomes. If something isn’t working, we change course.
Citizen-facing portals shipped since 2023: 14COTS Implementation & Integration
Salesforce. Atlassian. ServiceNow. Your agency already chose the platform. We make it perform. Certified engineers configure, customize, integrate, and train your team. No shelfware. No orphaned instances. Production-grade from day one.
COTS implementations: 22 · Shelfware: 0Data & AI Enablement
Machine learning and automation that survives your compliance review. We build data pipelines, predictive models, and decision-support tools inside FedRAMP boundaries. Every model is explainable. Every pipeline is auditable. Every deployment has a rollback plan.
ML models deployed in regulated environments: 11Who we work with.
- 01
State agencies
Direct contracts for licensing, elections, benefits and regulatory systems.
- 02
Local government
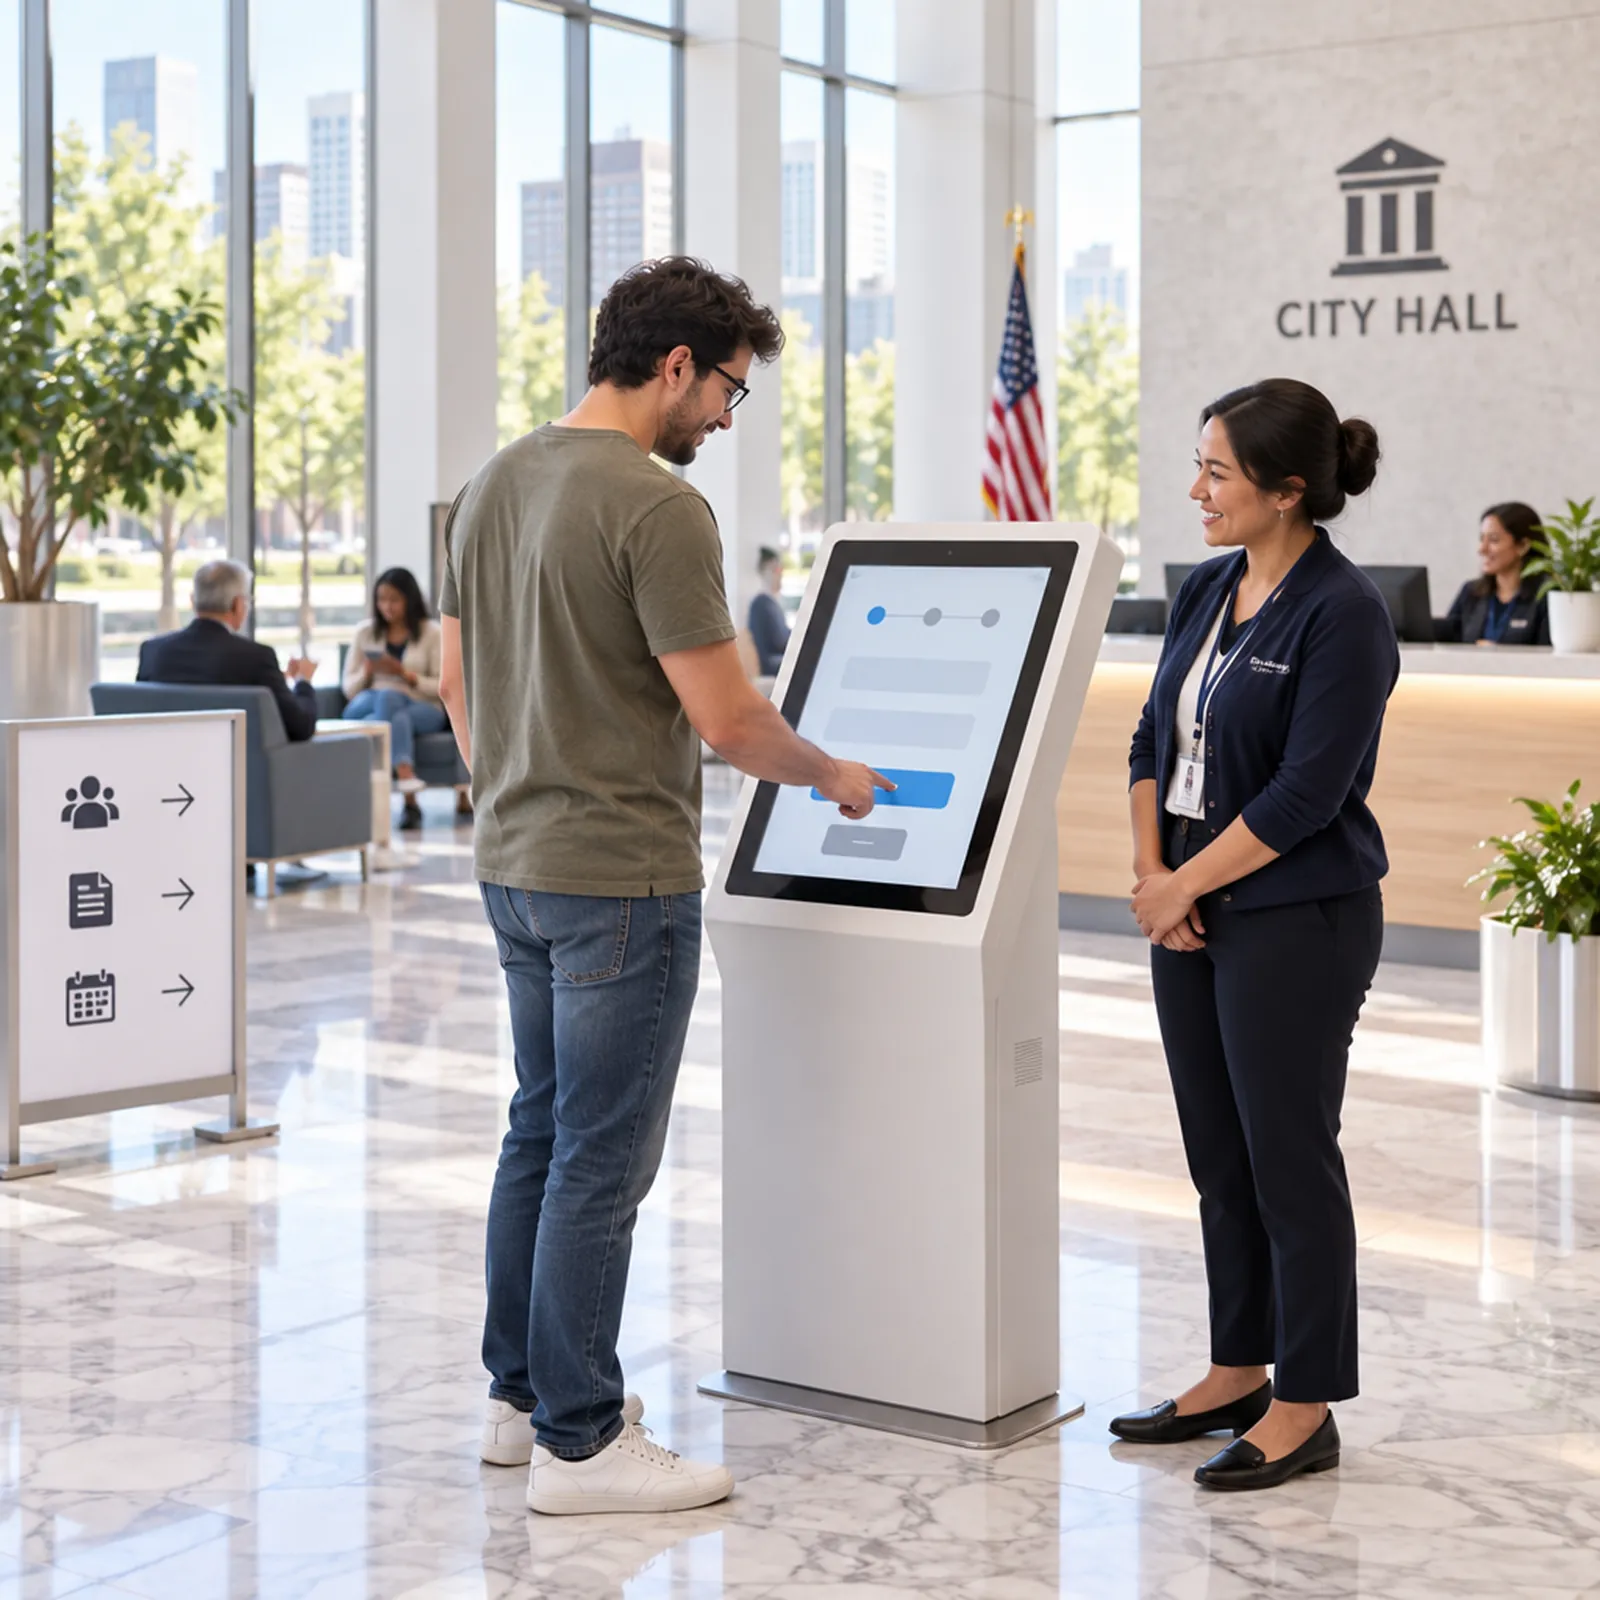
Cities and counties replacing paper processes and legacy portals.
- 03
Federal programs
Delivered through prime contractors. Our GSA MAS schedule is in progress.
- 04
Public authorities
Election offices, utilities and boards with public-facing duties.
How a government engagement runs.
- Stage 1
Capture & response
RFP and RFI responses in about 12 business days, with past performance and technical volumes.
- Stage 2
Discovery
One to two weeks of user research, control mapping and backlog planning.
- Stage 3
Build
Two-week sprints. Each one ends with working software, test results and control documentation.
- Stage 4
Authorization
SSP, control matrices and evidence packaged for your ATO review.
- Stage 5
Operate
A 90-day warranty, then optional managed service with SLAs.
How a resident’s request moves through a system we build
Every step writes to an audit trail, so evidence for reviews is collected automatically.
Credentials, not claims.
Every item below is backed by evidence in our capability statement.
| Framework | How we meet it | Status |
|---|---|---|
| NIST 800-53 | Every architecture decision documented against federal control families. | Aligned |
| FedRAMP-ready | Designed for inheritance into FedRAMP-authorized environments. | Ready |
| SOC 2 (Type II path) | Controls aligned; audit in progress. Attestation targeted for 2026. | In progress |
| Section 508 · WCAG 2.1 AA | Accessibility is a delivery requirement, not a post-launch remediation. | Shipped |
| HIPAA-ready | BAA-ready architecture. PHI handling documented per engagement. | Ready |
| StateRAMP-aligned | State agency workload design patterns. Documentation audit-ready. | Pattern-ready |
What your contracting officer needs.
- Entity name
- Bilions
- CAGE Code
- Available upon request
- UEI
- Available upon request
- NAICS
- 541511 · 541512 · 541519 · 541611 · 518210
- SAM.gov status
- Registration current, verification on request
- GSA MAS
- In progress
- Set-aside status
- Available upon request
- Contract vehicles
- BPA · IDIQ · T&M · Fixed-price · Subcontracting
- Security clearances
- Cleared engineer bench, levels disclosed per engagement
- Past performance
- CPARS references available under NDA
Featured government work.
Questions government buyers ask.
Do you hold active contracts with federal or state agencies?
We currently support active engagements with state-level authorities under NDA. Federal work is subcontracted through prime contractors for now; we’re pursuing a GSA MAS schedule.
What compliance frameworks do you align with?
NIST 800-53 (Rev 5), FedRAMP Moderate (pattern-aligned), StateRAMP, SOC 2 (Type II in progress), Section 508 / WCAG 2.1 AA, HIPAA, and PCI DSS where applicable.
Can Bilions prime, or only subcontract?
Both. We prime at the state level and subcontract on federal programs through teaming agreements with primes we’ve worked with before.
How fast can you respond to an RFP or RFI?
Most RFI responses go out within five business days. RFPs are typically seven to fourteen business days depending on requirements.
Do engineers have US citizenship or clearances?
All Bilions engineers are US-based. We maintain a cleared bench for engagements requiring Public Trust, Secret, or higher.
Will you sign agency-specific security addenda?
Yes. BAAs, DPAs, FISMA language, and agency-specific cybersecurity riders have all been through our legal review process before.
What is your approach to ATO (Authority to Operate)?
We design for ATO from sprint one, not as an afterthought. Engineers document control implementations as they build, and SSP templates align to your agency’s RMF workflow.
What is your pricing model?
Fixed-price, time-and-materials, or hybrid. Fixed-price engagements include milestone payments and our zero-overrun commitment on the defined scope. Managed service is available post-launch.
Do you provide post-deployment support?
Every engagement includes a 90-day warranty covering defects and critical issues at no additional cost. Extended managed service adds 24/7 monitoring, SLA-backed response, and quarterly patching.
How do you ensure knowledge transfer?
Documentation is a deliverable, not an afterthought. Every project produces runbooks, architecture decision records, and control matrices. Our goal is to make ourselves replaceable, that’s the definition of good delivery.
How do you handle CUI (Controlled Unclassified Information)?
Development environments enforce NIST 800-171 controls: encryption at rest and in transit, access logging and role-based access. Every engagement that touches CUI includes a documented handling plan.
What is your staffing model for government projects?
Senior engineers only. A typical team has a delivery lead, two or three full-stack engineers, a QA specialist and a security engineer. We never subcontract critical-path work without your approval.
Your first call is with a senior engineer from our team.